Hi all,
I maintain MoaV (Mother of all VPNs), an open-source, self-hosted, multi-protocol censorship-circumvention stack (Reality/VLESS/xray, Hysteria2, WireGuard/AmneziaWG, DNS tunnels, and more). One opt-in feature runs the official snowflake-proxy as a bundled donation service, so anyone who brings up a MoaV server for their own circumvention will also donate capacity to Snowflake from the same box with a single toggle. I also built a Grafana dashboard for snowflake so operators can see their contribution.
Some data from our test servers
- Proxy A: ~46,000 completed connections, ~236 GB relayed (running ~3 months)
- Proxy B: ~1,500 completed connections, ~24 GB relayed (~few weeks)
Together: ~47,500 connections and ~260 GB relayed to Snowflake clients.
Snowflake Grafana dashboard
For most services running in MoaV, we created a specialized Grafana dashboard, same goes for Snowflake.
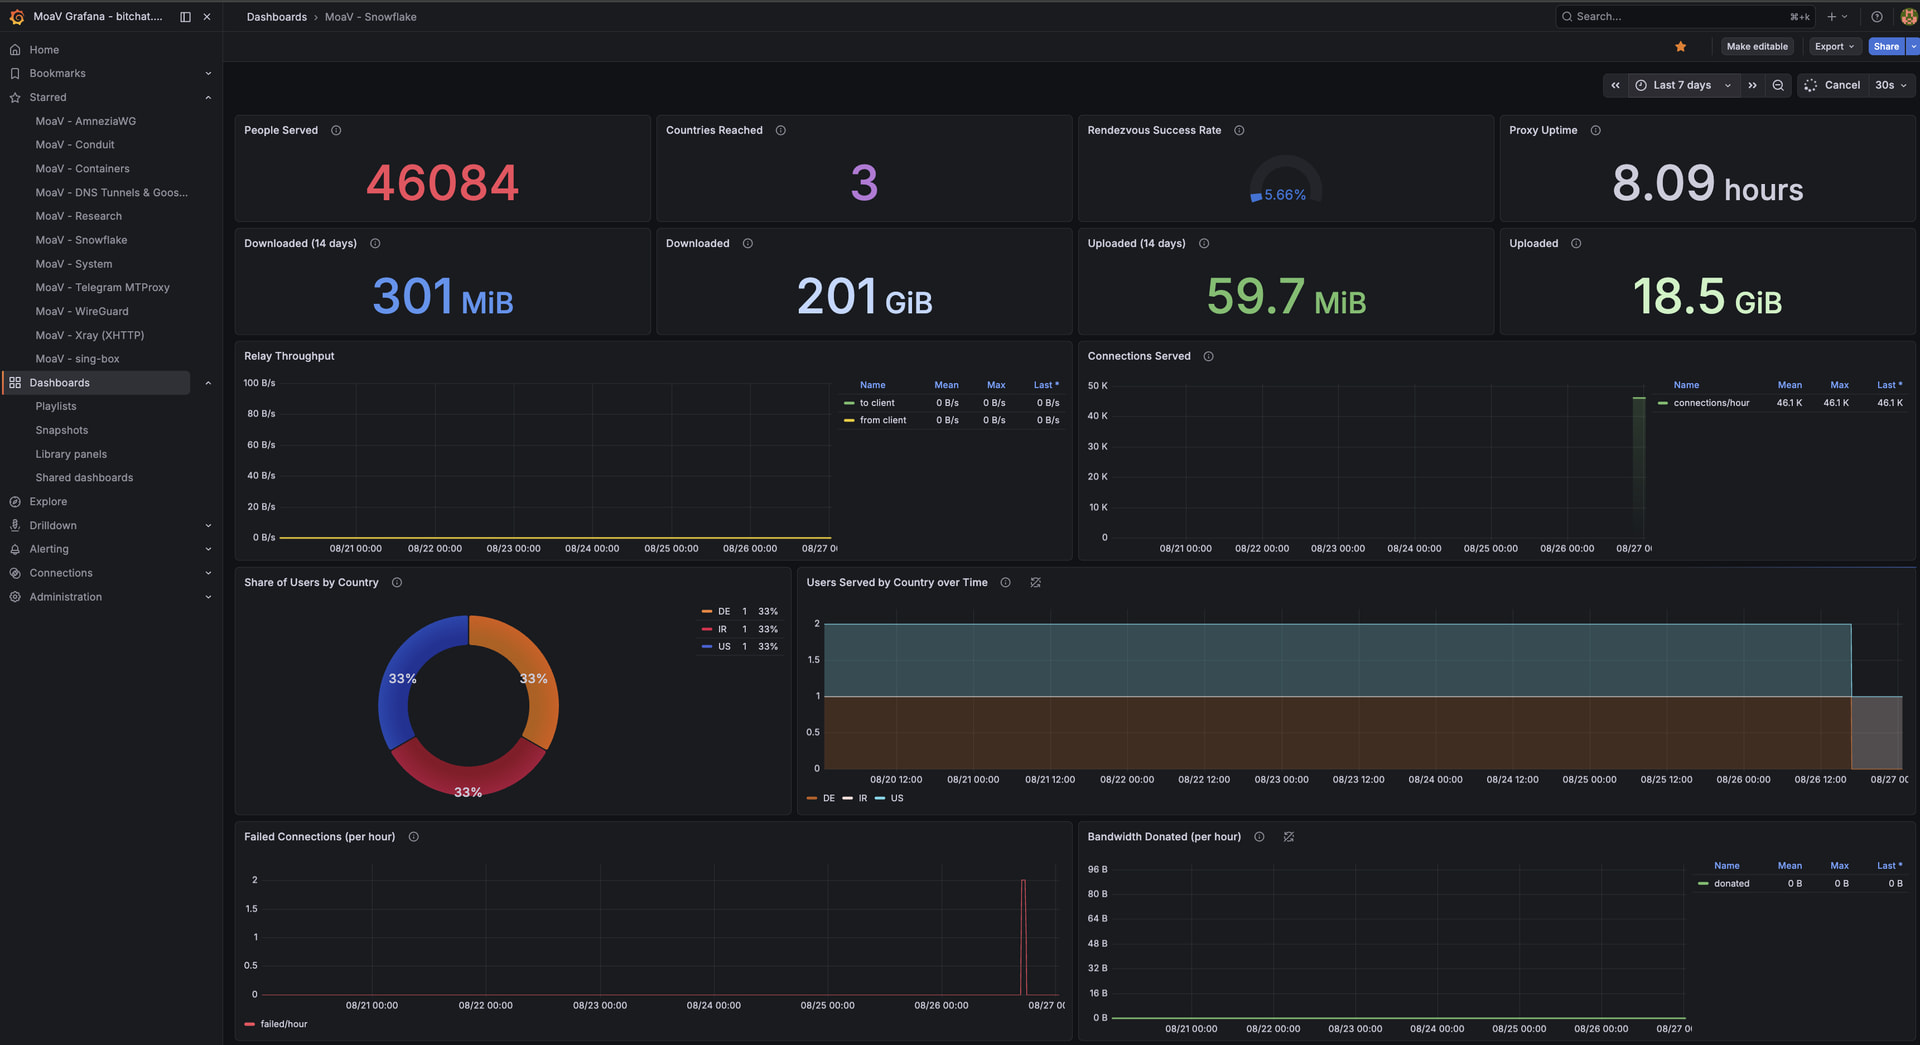
Panels: connection rate, up/down throughput, cumulative bytes relayed, client countries, and uptime. It reads the proxy’s periodic status line, so it works with a stock `snowflake-proxy`.
Questions
1. Traffic dropped to almost 0
Both proxies were genuinely busy for a couple of weeks (peaks around **12–13 GB/day each**), and then **both dropped to almost zero at essentially the same time**, around mid-month:
Proxy A — daily relayed (MB)
  07/30  6752
  08/05  8171
  08/06 10446
  08/08  5337
  08/10  4204
  08/11 12895
  ...then near-zero

Proxy B — daily relayed (MB)
  08/10   804
  08/11  1475
  08/12 13168
  08/13  7363
  08/14   155   <-- drops here
  ...then near-zero
The only thing that changed on our side is that both containers were recreated/updated to 2.14.1 on the same day the traffic died. We’re on the latest proxy (2.14.1), NAT is unrestricted, nothing errors in the logs, and a fresh restart re-registers fine.
what would cause two independent, unrestricted proxies to go from ~12 GB/day to near-zero right after a restart/update, and stay there? Is this expected broker behaviour (client assignment moving elsewhere, a reputation/warm-up effect after re-registration), or is there something a proxy operator commonly gets wrong on an update? What should we check first?
2. client-country counting.
For the grafana dashboard, I’ve implemented a geoip analytics, which works for other proxies like sing-box, xray, conduit, etc. However for Snowflake, after some initial head-banging-to-the-wall, I found out that tor-geoip-db has special format, and it “started to work”. Although as you can see in the screenshot, it shows 1 connection per country and usually never changes. This is probably an issue in the integration but how should the country data be interpreted: per completed connection, per unique client, or sampled? We want the panel to represent reach honestly. Any canonical reference is welcome.
I’m still tweaking the code to figure out many parts, and I would really appreciate any pointers or contributions to make the dashboards work properly.
- Snowflakes Grafana dashboard: MoaV/configs/monitoring/grafana/provisioning/dashboards/snowflake.json at dev · MotherofallVPNs/MoaV · GitHub
(You still need the exporter service docker for all the fields to show up, specially regarding historical numbers)
Thanks for building Snowflake.